Meet Arlo Siemsen: Distribution Engineer for the Rust Supply Chain
Since 2022, the Rust Foundation has run a Security Initiative aimed at the parts of the Rust ecosystem that no individual maintainer can reasonably be expected to cover alone: threat modeling for crates.io and the wider Project, provenance and artifact signing, trusted publishing, and tooling such as Painter and Typomania. Much of that work has been made possible through support from member organizations like AWS and through the funding of Alpha-Omega.
One of the largest efforts to come out of that initiative is artifact signing: a multi-year push to adopt The Update Framework (TUF) as the signing solution for crates.io and the Rust toolchain. TUF gives us a way to prove, cryptographically, that what a user installs is exactly what was published. While signing is important, what signing unlocks matters just as much, if not more: verified toolchains and crates.io mirrors.
About the Position
The Rust Foundation, through the gracious support of Alpha-Omega, is funding a Distribution Engineer dedicated to landing this work.
The role is focused on implementation. Specifically, the Distribution Engineer will:
- Integrate TUF and mirroring into Cargo, including the Cargo resolver. Part of this is coming to a consensus solution for specifying default mirrors and redirecting crates.io artifact requests to a configured mirror. There are competing approaches for Merkle tree proofs of crate verification, either via TUF directly or via the resolver, and both build on using TUF only for Merkle roots. We will experiment with them to see which meets our round-trip and bandwidth needs.
- Ship experimental, unstable features for mirrors and verification in Cargo and rustup. The goal is a working unstable mirroring solution that can fetch artifacts and verify their integrity against the existing index and an out-of-band TUF repository.
- Deploy an MVP TUF implementation for Rust releases: a prototype TUF repository providing signing for the release channel manifests and artifacts. It will be used strictly on rust-lang channel manifests and files, letting us self-verify our prototype mirror and test TUF’s scalability internally without directly affecting users.
- Support the Cargo team and rustup work with PR reviews and general help, as bandwidth allows.
Much of this is described in the Rust Project’s Implement Verifiable Mirroring Prototype goal, and everything shipped through it will initially land behind unstable feature flags. If it proves out, we will build more general, production-level mirroring support on top of it.
Meet Arlo Siemsen
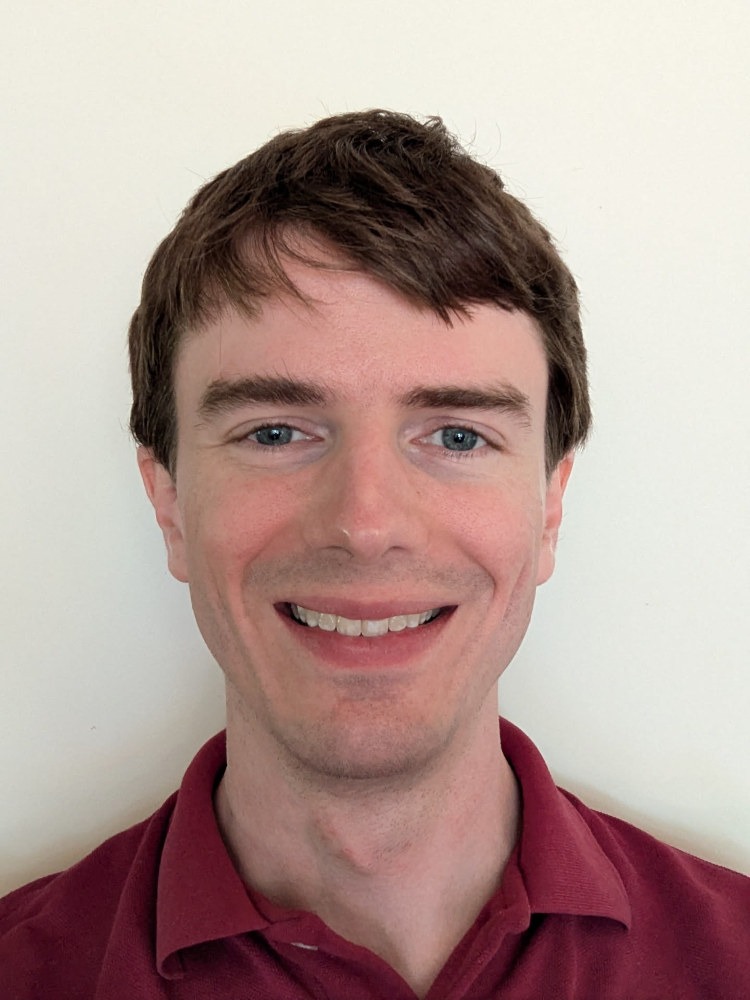
The Rust Foundation is glad to share that Arlo Siemsen is taking on this role. Arlo is already a member of the Rust Project’s Cargo team, and he has spent years working on areas where this project lives, the boundary between Cargo, crates.io, and how artifacts actually reach users.
He implemented Cargo’s sparse index protocol, which replaced the full git index clone with targeted HTTP requests and became the default for crates.io as of Rust 1.70. He designed and implemented Cargo credential providers and authenticated registries and he helps review security fixes for the Cargo team. Hear from Arlo in his own words below:
Hi! I’m Arlo Siemsen, or arlosi on GitHub. I started contributing to Cargo in 2021 working to improve the performance of fetching the crates.io index, which resulted in development of the sparse index protocol. The signing and mirroring work is a natural extension to further improve performance and trust, especially in bandwidth-constrained environments. I later developed Cargo credential providers and added authentication support for alternate registries. Outside Cargo, I enjoy writing Rust for embedded systems and microcontrollers.
Get in touch
If you run a Rust mirror today, or you need one and cannot make the current situation work, we want to hear from you. Discussion for this work happens in the #tbd-signing channel in the Rust Zulip, and you can reach the Foundation at mirroring at rustfoundation.org. We are especially interested in hearing from people operating mirrors in firewalled or bandwidth-constrained environments, and from CI providers carrying significant Rust traffic.
